

/ GitHub repo scanning
Paste a link to any public repo, including ones you don't own, like a take-home coding test or an open source tool. Ossprey scans the source and every package it pulls in, then gives you a verdict before anyone runs it.
Repos you don't own
Scan any public repo on GitHub, whoever owns it.
Source and dependencies
Ossprey reads the repo's own code and every package it installs.
A verdict with evidence
Every finding is graded and comes with a threat report showing what the code does.
/ Supply chain threat detection

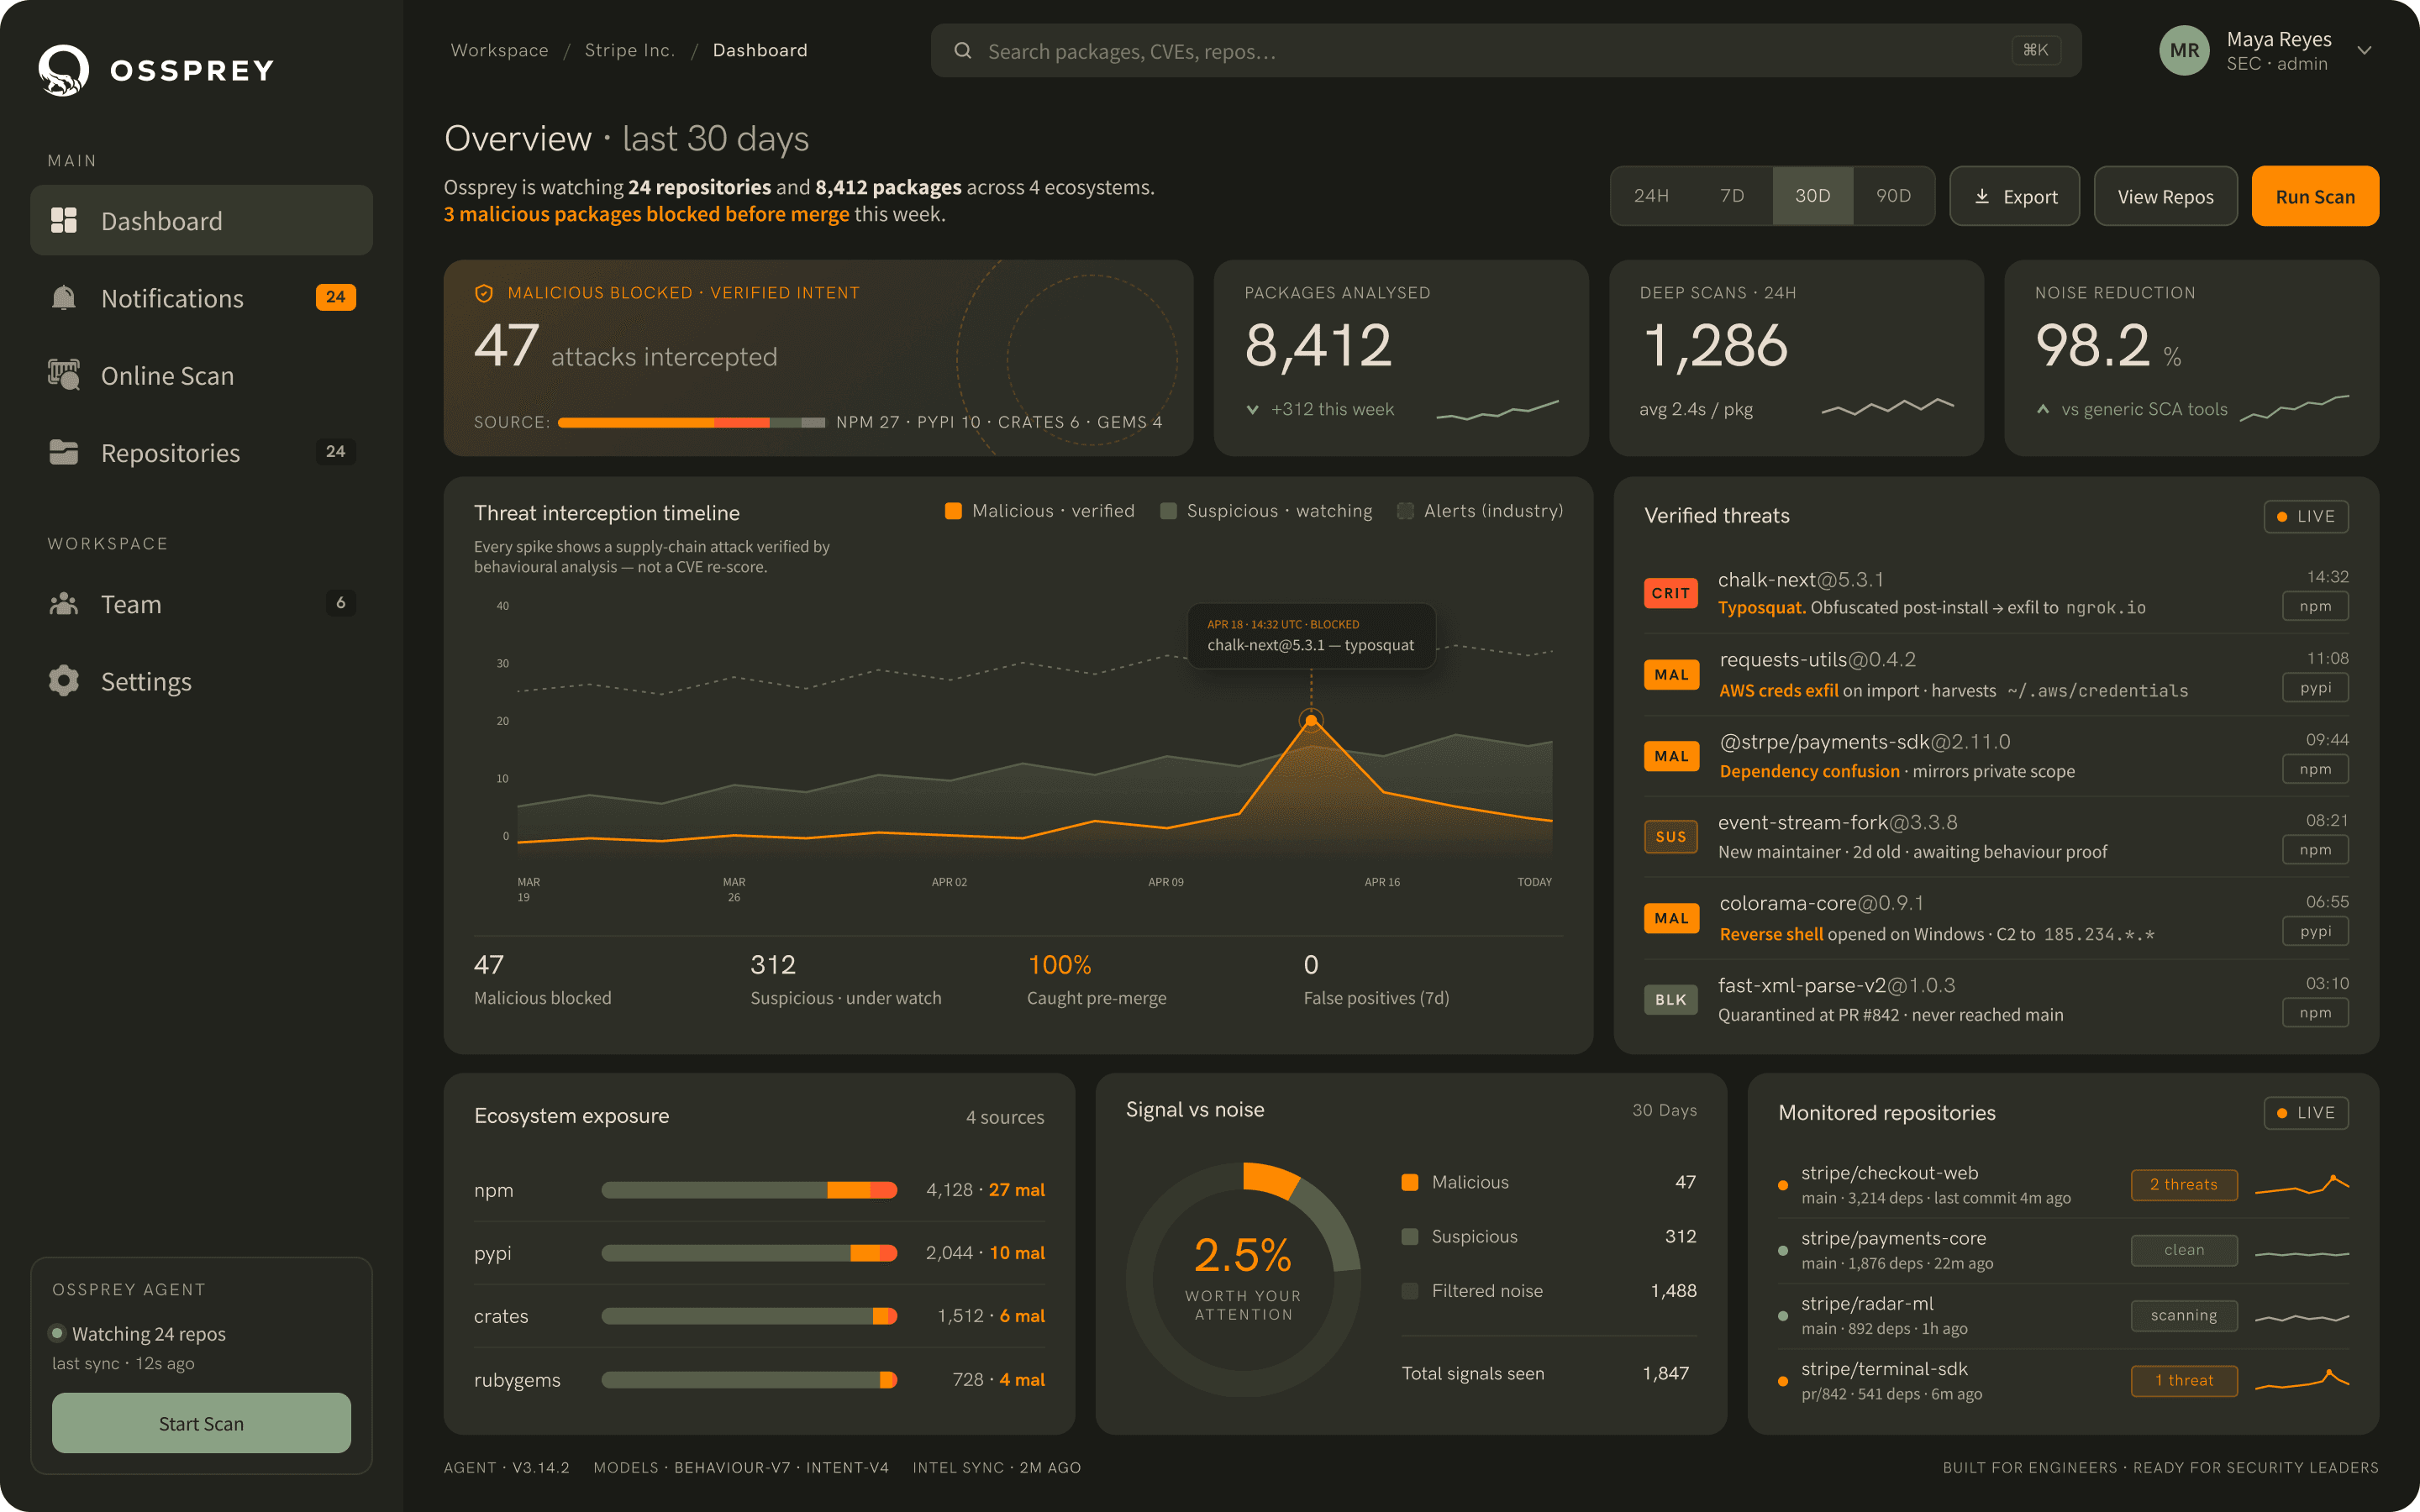

/ Developer-first workflow
1
Scan GitHub repos, packages and dependencies.

2
Understand what code actually does.

3
Only real threats, with context.

4
We watch your repos in the background.

GitHub App Install
Runs alongside your existing dev environment. No infrastructure changes. Works with your stack from day one.
Doesn't slow your build or gate your deployments. Ships with you, not in front of you.
Not a report to read at the weekend. A specific finding, with context, telling you exactly what to look at and why.
/ APIs
GitHub
Security findings surfaced as PR checks. Review risk before it merges.

GitHub Actions
Runs behavioural analysis as part of your existing CI workflow.
Slack
Real-time alerts in the channel your team already watches and with everything you need to investigate in the dashboard.
Jira
Findings automatically create tickets with full context. Straight into your existing remediation workflow.
API
Full API access. Build Ossprey data into your own tooling, dashboards, or security workflows.
More coming
Early access. Tell us what you need and we'll prioritise it.
/ Try It Free
Most teams are up and running in under 15 minutes.
Book a Demo · Try It Free
